Security First
Protecting organizations through modern security practices and secure technology delivery.
Security is built into every service we deliver. Here is how each layer of protection works, explained for both business and technical readers.
Identity Security
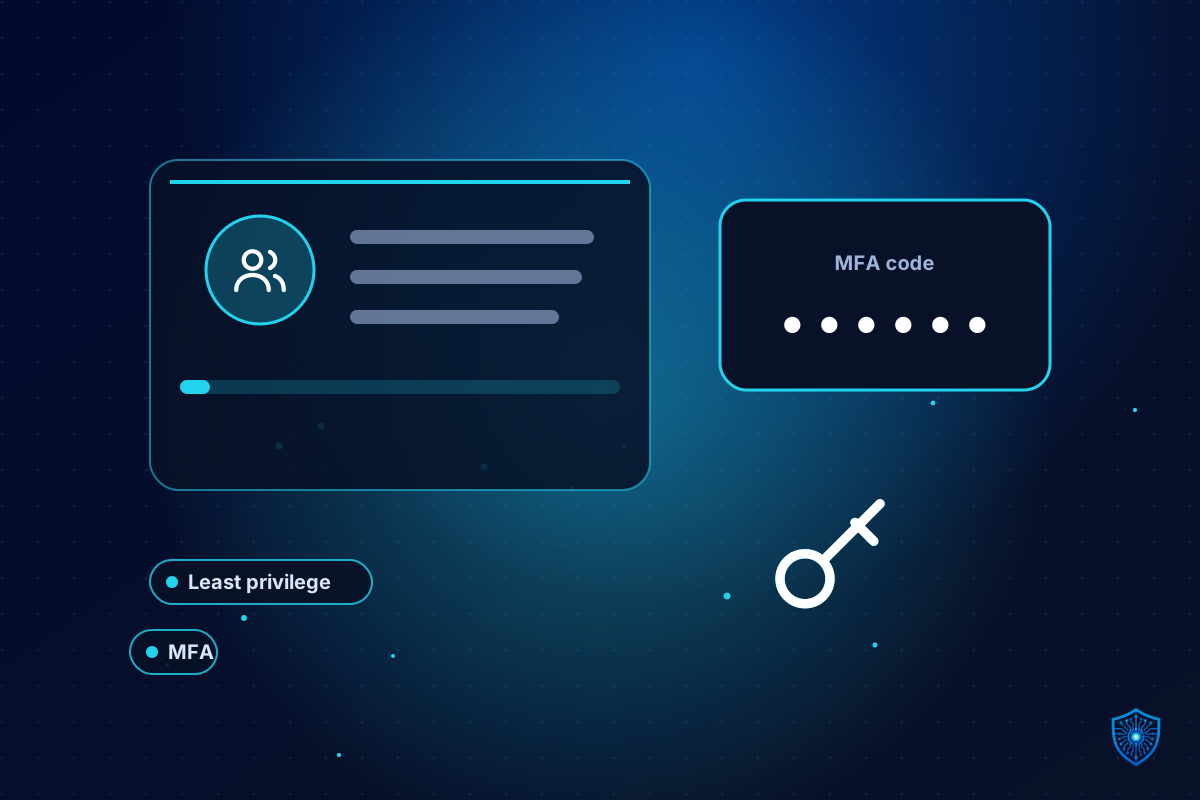
Most attacks start with stolen passwords. We make sure only the right people, on the right devices, can get in.
MFA for all users, phishing-resistant methods for admins, Conditional Access, privileged access management, access reviews and joiner-mover-leaver automation.
Cloud Security
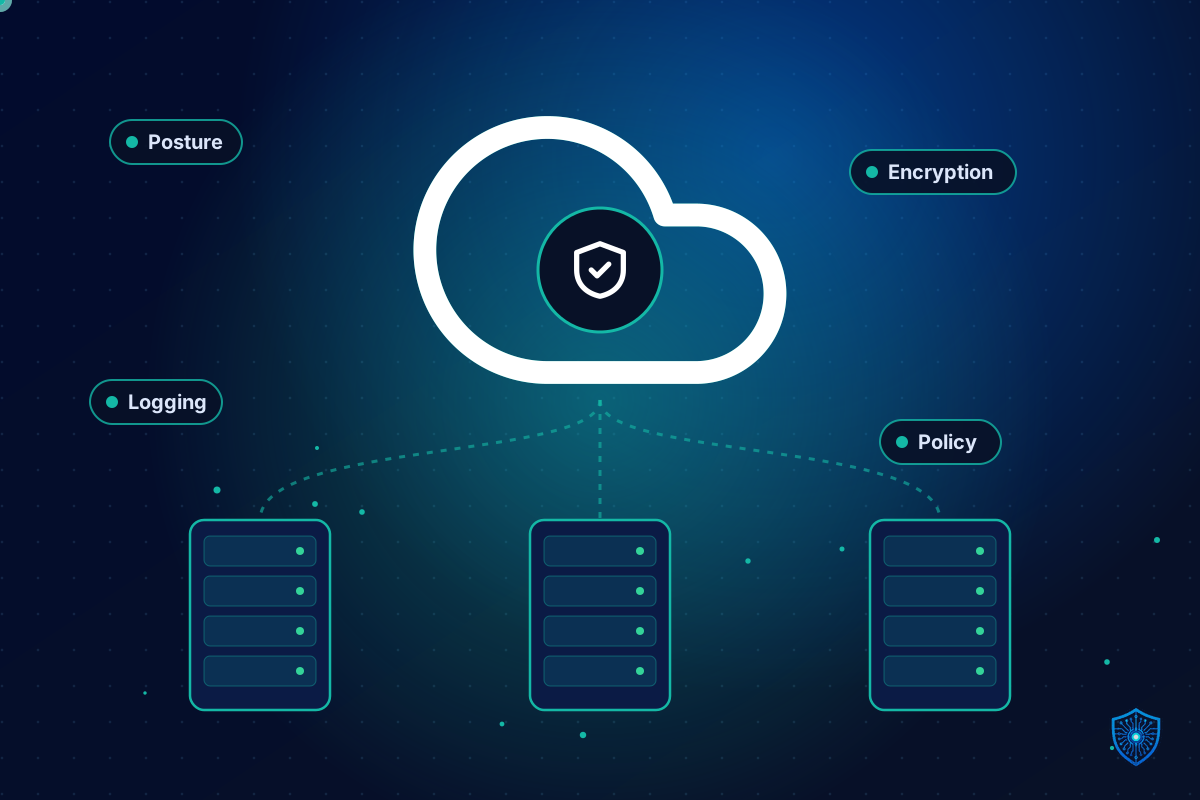
Your cloud should be configured securely from the start, and stay that way as it changes.
Landing zone guardrails, posture management, encryption and key management, network isolation with private endpoints, logging to a central SIEM and policy as code.
Endpoint Security
Laptops, phones and servers are protected, patched and monitored wherever they are.
Device management, disk encryption, EDR with managed response, patch SLAs, application control and secure baseline configurations.
Application Security
Software is built and tested so that weaknesses are found before customers or attackers find them.
Secure SDLC, code review, SAST/DAST and dependency scanning, secrets management, API security testing and penetration testing before release.
Network Security
Traffic is controlled and monitored so an issue in one place cannot spread everywhere.
Firewalls, segmentation and microsegmentation, VPN or Zero Trust network access, IDS/IPS, DNS filtering and flow logging.
Compliance Security
Security controls are mapped to the frameworks your customers and regulators ask about.
Control mapping across SOC 2, ISO 27001, HIPAA, NIST, PCI DSS, NIS2 and DORA, with evidence collection and audit readiness support.
Security of this website
- HTTPS across the entire site
- Web application firewall and malware scanning
- Brute-force login protection and MFA for administrators
- Automated backups
- Security headers
To report a security concern, email info@itguiders.com.
Ready To Transform Your Technology Strategy?
Talk to an expert about your goals. No obligation, direct access to specialists.